Questions / Answer
What Is the Difference Between an Agency ATO and a JAB P-ATO?
Your SaaS product wants federal customers, but the old authorization paths keep getting mixed up.
For years, FedRAMP had two paths to authorization. One was an Agency ATO. The other was a JAB P-ATO. The difference came down to who signed the paper.
What does FedRAMP stand for?
FedRAMP means Federal Risk and Authorization Management Program.
It is the United States program that checks if a cloud service is secure enough for federal agencies. A cloud service provider (CSP) is the company selling the service. A Third-Party Assessment Organization (3PAO) is the independent auditor that tests the service.
What is an Agency ATO?
ATO means Authorization to Operate.
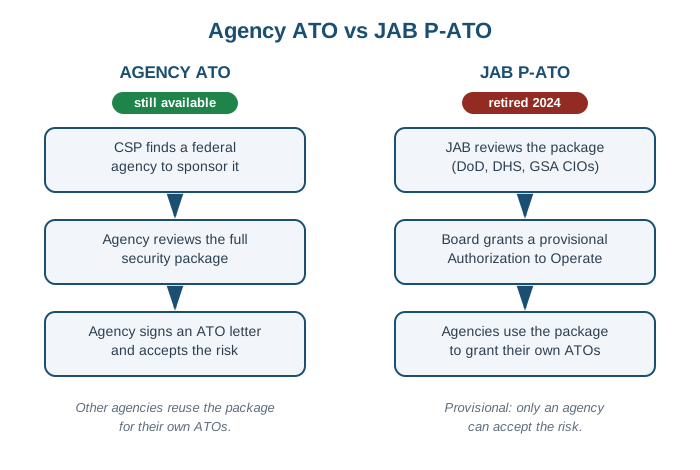
In the Agency path, one federal agency agrees to sponsor the cloud service. The sponsor agency reviews the full security package. If the service passes, the agency signs an ATO letter and accepts the risk.
That ATO covers that agency's use. Other agencies can reuse the same security package to grant their own ATOs.
The package includes the System Security Plan, or SSP. It includes the Security Assessment Report, or SAR. It includes the Plan of Action and Milestones, or POA&M, which lists weak spots and fixes. FedRAMP's own legacy documentation lists all of these as required package parts.
What was a JAB P-ATO?
JAB means Joint Authorization Board.
The JAB brought together the chief information officers of three federal bodies. Those bodies were the Department of Defense, the Department of Homeland Security, and the General Services Administration.
P-ATO means Provisional Authorization to Operate. It was provisional for one reason. The JAB could not accept risk for any agency. Only an agency can do that. So the P-ATO was a strong board-level recommendation, not a real ATO. Agencies read the JAB-reviewed package and then granted their own ATOs.
In practice, the P-ATO worked like a head start. One board review saved every interested agency from starting over. The provisional label exists because only an agency can accept risk for its own use. FedRAMP\u2019s own legacy documentation frames each path this way.
What happened to the JAB?
The JAB path is gone.
In July 2024, OMB (the Office of Management and Budget) issued memorandum M-24-15 to modernize FedRAMP. The JAB then shut down for nearly a year. That shutdown is described in FedRAMP's own review of fiscal year 2025.
FedRAMP replaced the JAB authorizations with a new Program authorization path. The FedRAMP Board now handles governance and oversight. It does not approve individual packages the way the JAB did.
In June 2026, FedRAMP published its Consolidated Rules for 2026. The rules made the single official label "FedRAMP Certified." They define two paths: Program and Agency. New JAB P-ATOs are no longer issued.
Which path should my company pick today?
Follow the sponsor.
If a federal agency already wants your product, pursue the Agency path with that sponsor. The agency knows its risk rules, and it signs the ATO itself.
If no agency has signed on, the Program path was built for your situation. FedRAMP's own review says the lack of sponsorship blocked new services for years. The Program path gives those services a route forward.
Forget the JAB P-ATO in your planning. It no longer exists as a path.
Practical steps in order:
- Talk to agencies already using or evaluating your product.
- If one agrees to sponsor, start the Agency path with them.
- If none will, study the Program certification path on fedramp.gov.
- In either case, start collecting control evidence now. Every path needs it.
Where does evidence collection fit in?
Both paths demand proof for every control.
Tools that pull live configuration data from your cloud environment cut the manual work. PolicyCortex is one such tool. Its 33 collectors read live Azure configuration. It is evaluated against NIST 800-53 and NIST 800-171. It generates SSP, SAR, and POA&M output from collected evidence. It supports re-verification after remediation. It is strongest in commercial Azure, and it covers AWS.
Note: PolicyCortex is not FedRAMP authorized.
Next step
See how automated evidence collection shortens the authorization process.
Sources
- FedRAMP, "FedRAMP Built a Modern Foundation in FY25 to Deliver Massive Improvements in FY26," September 30, 2025, https://www.fedramp.gov/2025-09-30-fedramp-built-a-modern-foundation-in-fy25-to-deliver-massive-improvements-in-fy26/
- FedRAMP, "FedRAMP Certification," Consolidated Rules for 2026, https://www.fedramp.gov/2026/providers/20x/rules/fedramp-certification/
- FedRAMP, "Initial Outcome from RFC-0020 FedRAMP Authorization Designations," https://www.fedramp.gov/rfcs/0020/
- FedRAMP legacy documentation, "What's in an Authorization Package," https://www.fedramp.gov/legacy/playbook/csp/authorization/what/