Questions / Answer
A Management Plane Zero-Day Tests Incident Response and Flaw Remediation
The Federal Risk and Authorization Management Program (FedRAMP) runs on two promises. You fix serious flaws fast. You respond to incidents with evidence.
A software-defined wide area network (SD-WAN) links branch sites over shared connections. VeloCloud Orchestrator (VCO) is the web console that manages it. Arista confirms active exploitation of a flaw in on-premises VCO. The flaw is tracked in the Common Vulnerabilities and Exposures program as CVE-2026-114625.
The flaw your plan must handle
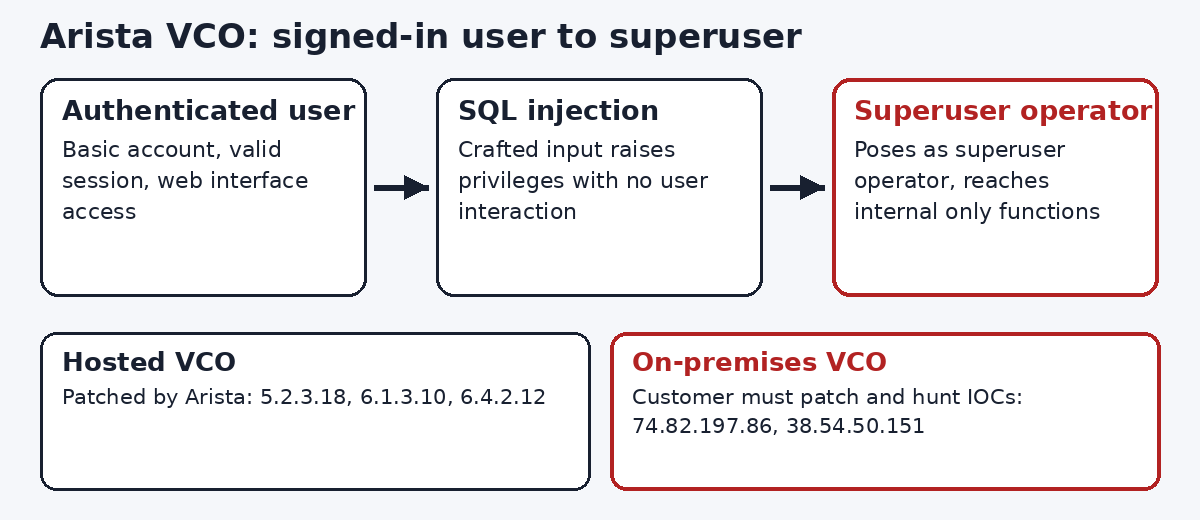
A user signs in with basic privileges. A Structured Query Language (SQL) injection path raises privileges. Any authenticated user can gain operator rights. That user can pose as a local superuser operator.
The path reaches functions meant for internal use only. Arista says exploitation may harm the orchestrator. It may also harm the data the orchestrator manages.
Flaw remediation, with dates
Remediation evidence needs versions and dates. Arista patched its hosted service already. The patched levels are 5.2.3.18, 6.1.3.10, and 6.4.2.12. A hosted customer records the vendor attestation.
An on-premises operator owns the patch work. Record the starting version and the fixed version. Record the scan that verifies the fix. Open a Plan of Action and Milestones (POA&M) entry if dates slip.
PolicyCortex does not patch Arista gear. Your remediation record should name who does.
Incident response, with artifacts
Patching alone does not close an exploited flaw. Arista published indicators of compromise (IOCs). The two Internet Protocol (IP) addresses are 74.82.197.86 and 38.54.50.151. Hunt both in connection and access logs.
Arista advises preserving logs before remediation. Save web, backend, system, and database logs. Save file system timestamps as well. Review administrator activity for unusual changes.
The governance lesson
Management planes are part of the system. Inventory every orchestrator inside your boundary. Governance means you fully understand the layer that configures the rest.
What to do this week
Confirm each orchestrator version against the patched levels. Run the IOC hunt and file the artifacts. Update the POA&M entry with real dates.
Sources
- Arista Security Advisory 0199, October 22, 2026.
- CVE-2026-114625 record, CVE Program. The record is in reserved state at publication time.
- BleepingComputer, Arista patches new VeloCloud Orchestrator zero-day. https://www.bleepingcomputer.com/news/security/arista-patches-new-velocloud-orchestrator-zero-day-exploited-in-attacks/
- NIST SP 800-53 Revision 5, Security and Privacy Controls. https://doi.org/10.6028/NIST.SP.800-53r5
- Original diagram by PolicyCortex.
Next step
Want remediation evidence that updates itself from scans? See how PolicyCortex tracks it on Azure.