Questions / Answer
Two Hours From Advisory to Attack: The Flaw Remediation Clock That Matters
CVE is Common Vulnerabilities and Exposures. CVE-2026-21589 is an unauthenticated arbitrary file access flaw in eight Atlassian Data Center products.
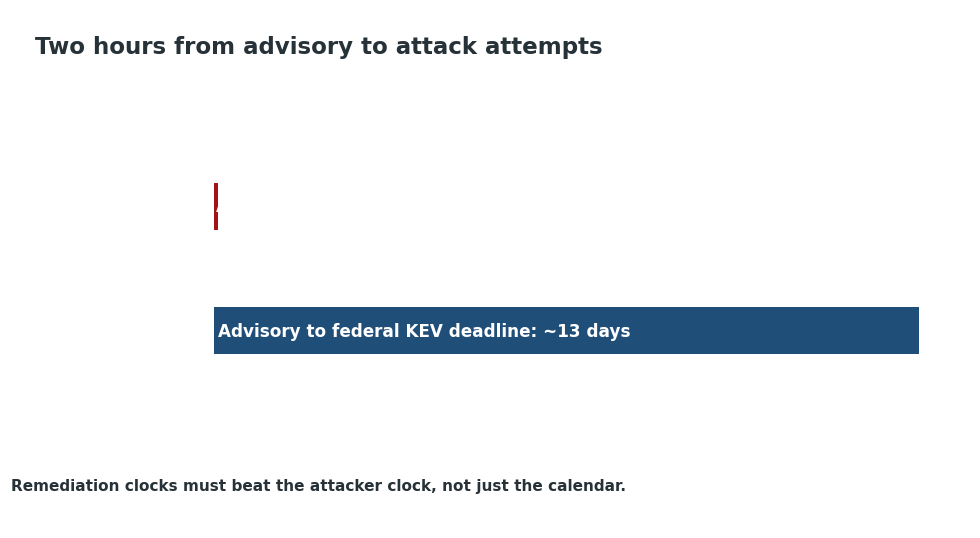
Atlassian published the advisory on October 5, 2026. Rapid7 reported exploitation attempts within about two hours. Public proof of concept scripts exist.
The two clocks side by side
CISA is the Cybersecurity and Infrastructure Security Agency. CISA added the flaw to its Known Exploited Vulnerabilities catalog on October 15, 2026. Federal agencies had until October 18 to remediate.
That is a 13 day window from advisory to deadline. The attacker window was two hours. The gap between those two numbers is the whole lesson.
Its CVSS score is 9.3, Critical. CVSS is the Common Vulnerability Scoring System. Critical flaws with live exploits deserve the fastest remediation timeframe your plan allows.
What continuous monitoring should do
FedRAMP continuous monitoring tracks vulnerabilities on a defined cycle. High risk findings get short clocks. This flaw is the case for using the short clock.
Monitor the shared component, not just the products. The atlassian-plugins-webresource component ships inside all eight. One scan of the component covers Bitbucket, Confluence, Jira Software, Jira Service Management, Bamboo, Crowd, Crucible, and Fisheye.
Verify the fix after install. Keep the scan that shows CVE-2026-21589 is gone. The monthly report should show the finding closed with evidence, not with a ticket number.
Fixed builds
Bitbucket 9.4.26, 10.2.8, 10.5.1. Confluence 9.2.26, 10.2.19. Jira Software 9.12.40, 10.3.26, 11.3.12.
Jira Service Management 5.12.40, 10.3.26, 11.3.12. Bamboo 10.2.24, 12.1.12. Crowd 6.3.7, 7.0.3, 7.1.7, 7.2.4. Crucible 4.9.15. Fisheye 4.9.15.
Sources
- Atlassian security advisory for CVE-2026-21589, Atlassian, October 5, 2026. https://confluence.atlassian.com/security/cve-2026-21589-arbitrary-file-access-vulnerability-impacts-multiple-products-1870495748.html
- CVE-2026-21589 record, CVE Program.
- Emergency Threat Response: CVE-2026-21589, Rapid7. https://www.rapid7.com/blog/post/etr-cve-2026-21589-critical-unauthenticated-arbitrary-file-access-in-atlassian-products/
- CERT-EU Security Advisory 2026-015, CERT-EU. https://cert.europa.eu/publications/security-advisories/2026-015
- Original diagram by PolicyCortex.
More continuous monitoring guides live at fedramp.net.
Check whether your flaw remediation plan has a same-day tier for critical flaws with live exploits.