Questions / Answer
BeyondTrust KEV Flaw Sets a FedRAMP Remediation Clock
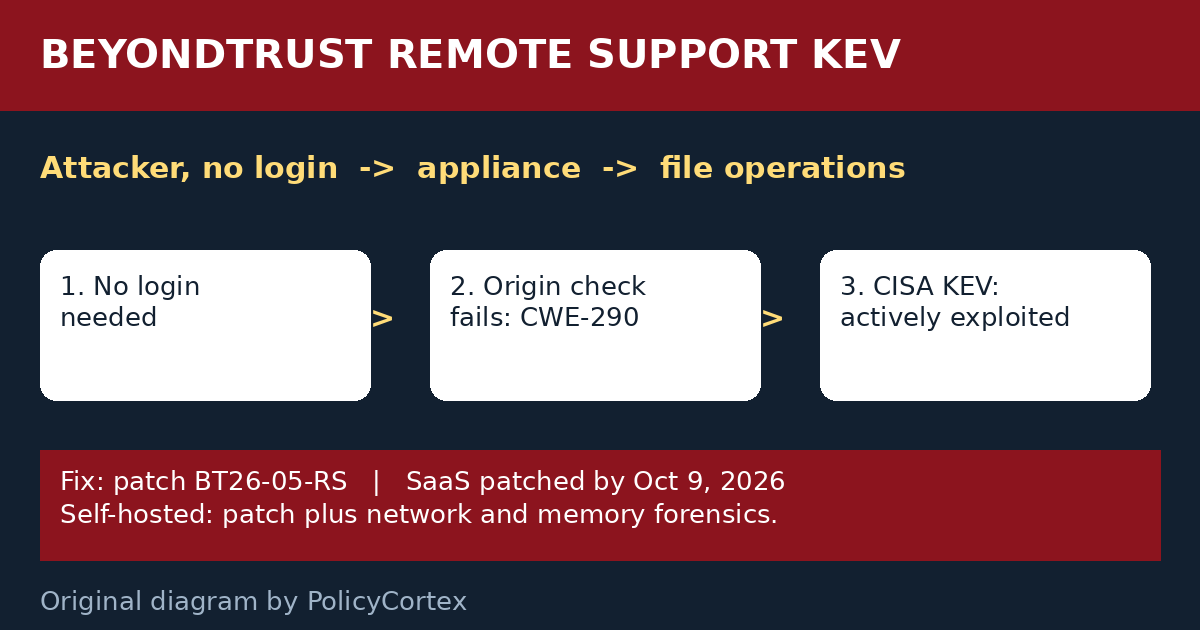
A KEV listing is a clock with a date on it. This one already rang.
On October 15, 2026, BeyondTrust published security advisory BT26-05. It fixes a flaw in Remote Support scoring 9.3 under Common Vulnerability Scoring System (CVSS) version 4.0. A remote attacker with no login can perform file operations on the appliance. The weakness is Common Weakness Enumeration (CWE) 290, improper origin validation.
The flaw and the KEV listing
Common Vulnerabilities and Exposures (CVE) is the public record system.
- CVE-2026-102764: improper origin validation flaw in an internal messaging component. A remote attacker with no login can perform file operations on the appliance.
All Remote Support versions 26.2.3 and earlier are affected. The Cybersecurity and Infrastructure Security Agency (CISA) added it to its Known Exploited Vulnerabilities (KEV) catalog. That listing came on October 16, 2026. The due date was October 19, 2026. That date has now passed. An unpatched appliance is past due, not just at risk.
CISA says threat actors are actively exploiting the flaw. They use it to gain initial access, then establish persistence, escalate privileges, and move laterally.
How to run the clock
Open one ticket per appliance. Record the advisory date, October 15, 2026. Record the KEV date, October 16, 2026. Record the due date, October 19, 2026. List the version on each appliance. Record the patch date for patch BT26-05-RS. Note any upgrade done first for versions older than 24.3.1.
Close the ticket only with two items attached. The dated patch record. The network and memory forensics result CISA urges for self-hosted appliances. BeyondTrust patched SaaS customers by October 9, 2026. Self-hosted tickets stay open until both items land.
Sources
- BeyondTrust security advisory BT26-05, BT26-05, October 15, 2026.
- CISA alert, CISA Urges Patching Critical Vulnerability in BeyondTrust Remote Support, October 16, 2026.
- CISA Known Exploited Vulnerabilities catalog, Known Exploited Vulnerabilities Catalog, listing dated October 16, 2026.
- CVE-2026-102764 record, CVE Program.
- Original diagram by PolicyCortex.
Next step
Want remediation clocks tracked without chasing spreadsheets? See how PolicyCortex collects it from live systems.