Questions / Answer
Cisco UC Flaws and the Flaw Remediation Clock
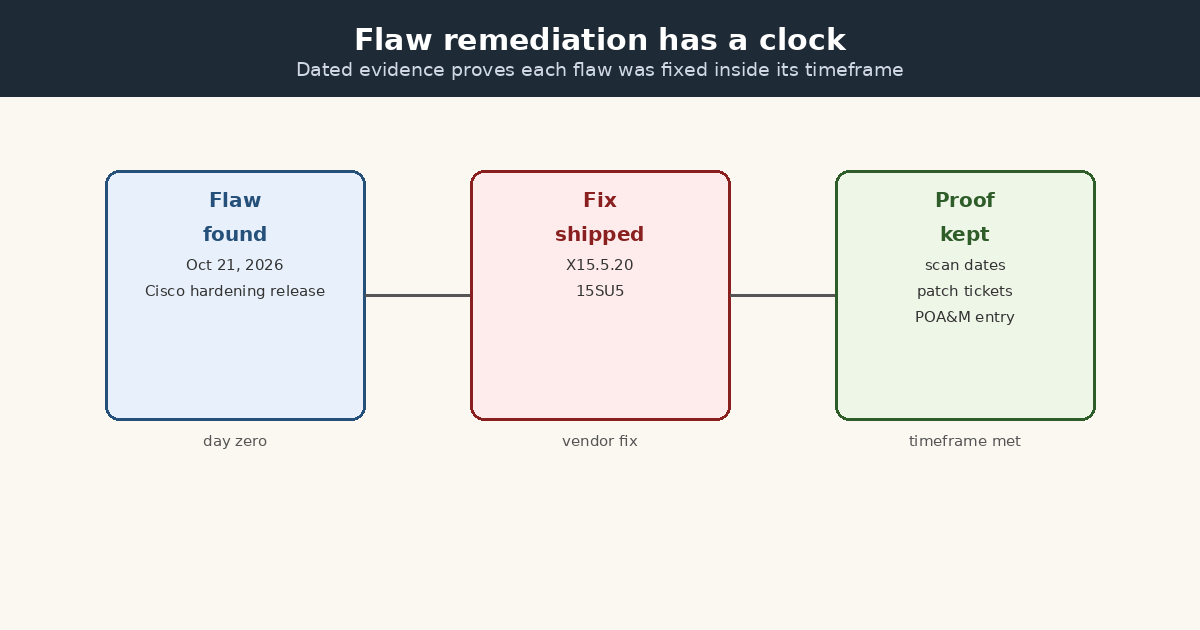
Flaw remediation has a clock. The clock starts when the flaw is disclosed. Cisco disclosed a serious batch on October 21, 2026.
The evidence must show each affected system was fixed inside its timeframe. That evidence is dated proof, not a plan.
What Cisco disclosed
The headline record is CVE-2026-76466. Common Vulnerabilities and Exposures (CVE) is the record system.
It is an unauthenticated remote code execution flaw in clustered Cisco Expressway. An attacker can run OS (operating system) commands as root. Cisco scores it 9.8 under CVSS (Common Vulnerability Scoring System) 3.1. The fix is X15.5.20.
The Unified Communications hardening advisory carries eight CVEs. Two score 9.8: CVE-2026-76473 and CVE-2026-76474. The fix is release 15SU5.
The Snort 3 hardening advisory carries four grouped CVEs. CVE-2026-20043 scores 9.0. Fixes land in Snort 3.12.4.0 and Cyber Vision 5.6.0.
Cisco lists no workarounds. Cisco knows of no malicious use as of October 21, 2026.
How the timeframe works
Remediation timeframes are set by severity. Higher scores get shorter clocks. A 9.8 is at the top of that scale.
The clock runs per affected asset. Each Expressway node and each Unified CM server needs its own dated fix record. A single ticket can cover many assets if it names each one.
When a fix cannot land in time, the delay needs a plan of action. The plan names the asset, the risk, and the target date. The plan is itself dated evidence.
The evidence to keep
Keep the advisory publication date as day zero. Keep scan results that show which assets were affected. Keep patch tickets with before and after versions and completion dates.
Keep a closing scan that confirms the fix. For cloud-managed assets, keep the vendor update record. Cisco says its cloud firewall and Secure Access were updated automatically.
PolicyCortex does not patch Cisco products. Your team applies vendor fixes. PolicyCortex helps collect the dated remediation proof.
What to do this week
Inventory every affected Cisco asset. Open one dated ticket per fix wave. Record before and after versions as each asset completes.
Sources
- CVE-2026-76466 record, CVE Program.
- Cisco Security Advisory cisco-sa-vcs-static-cred-hr7EWZ8t, Cisco Expressway Series Remote Code Execution Vulnerability, October 21, 2026. https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-vcs-static-cred-hr7EWZ8t
- Cisco Security Advisory cisco-sa-voice-hardening-twgbH9e3, Cisco Unified Communications Products Security Hardening Release: October 2026, October 21, 2026. https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-voice-hardening-twgbH9e3
- Cisco Security Advisory cisco-sa-hardening-snort3-ybgmhTQe, Snort 3 Security Hardening Release: October 2026, October 21, 2026. https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-snort3-ybgmhTQe
- Original diagram by PolicyCortex.
Next step
Want remediation evidence with dates your assessor can follow? See how PolicyCortex collects it from live systems.