Questions / Answer
A Three Day KEV Clock Against FedRAMP Remediation Timelines
FedRAMP continuous monitoring runs on clocks. Every scan finds flaws. Every flaw gets a remediation window. The windows shrink as risk rises.
The Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-110447 to its Known Exploited Vulnerabilities (KEV) catalog on October 23, 2026. Common Vulnerabilities and Exposures (CVE) is the public record system. The federal due date is October 26. That is three days.
The flaw and its score
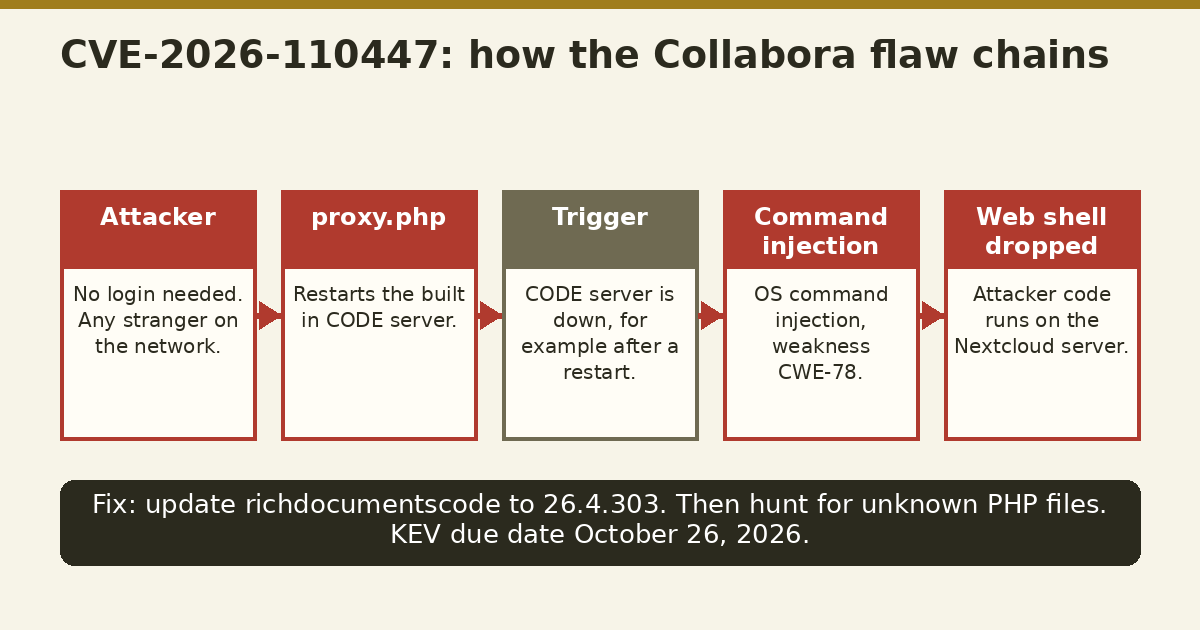
The flaw is an OS command injection in the Collabora Online Built-in CODE Server, a Nextcloud app called richdocumentscode. When the CODE server is not running, for example after a restart, proxy.php passes input to an operating system command.
The CVE record scores it CVSS 4.0 9.2. The Common Vulnerability Scoring System (CVSS) is the severity scale. A 9.2 is critical. Versions before 26.4.303 are affected.
FedRAMP remediation timelines treat critical flaws as the top tier. The KEV clock is even tighter. Either way, this flaw lands in the shortest window you have.
What the monitoring package should show
Your monthly conmon package should name this CVE directly. Continuous monitoring (conmon) is the monthly evidence cycle. The package should show the scan that found it, the ticket that tracked it, and the patch that closed it.
Exploitation ran in the wild in September and October 2026. Attackers dropped web shells on real servers. So the package should also show the compromise check. A file hunt in the app folder. A log review for proxy.php hits. A clean scan after the 26.4.303 update.
If the flaw is still open at month end, it belongs on the Plan of Action and Milestones (POA&M). A POA&M tracks known flaws and their fixes. Note the KEV due date on the entry. It shows the authorizing official you knew the real clock.
PolicyCortex does not patch Nextcloud apps or clean web shells. Your team applies vendor fixes. PolicyCortex helps organize the evidence that follows.
What to do this week
Patch richdocumentscode to 26.4.303. Record the before and after versions for the conmon package.
Sources
- CVE-2026-110447 record, CVE Program.
- CVE-2026-110447 detail, National Institute of Standards and Technology.
- CISA KEV catalog, added October 23, 2026, due October 26, 2026.
- Nextcloud community forum notice, "To Collabora Built-in User: Update ASAP," October 3, 2026.
- Original diagram by PolicyCortex.
Next step
Want conmon evidence assembled from live systems each month? See how PolicyCortex collects it automatically.