Questions / Answer
GitLab RCE and FedRAMP Flaw Remediation Timelines
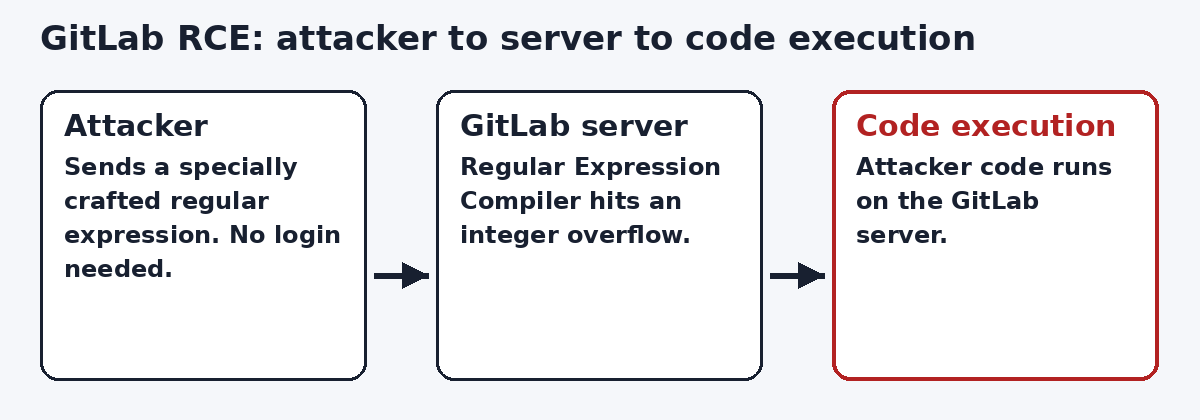
Development tooling sits inside many cloud service boundaries. A critical flaw there is not a minor internal matter.
The Federal Risk and Authorization Management Program (FedRAMP) expects fast flaw handling. CVE-2026-110264 is the kind of flaw that tests it. The Common Vulnerability Scoring System (CVSS) score is 10.0, Critical.
The flaw on the record
The Common Vulnerabilities and Exposures record cites an integer overflow. GitLab triggered it by compiling a specially crafted regular expression.
The outcome is remote code execution (RCE) on the server. Under certain conditions, the user needed no authentication.
Both GitLab Community Edition (CE) installations are affected. Both GitLab Enterprise Edition (EE) installations are affected. The range starts at version 7.0, before 18.11.13. Each 19.x release line is affected before its fix.
GitLab published fixed releases on October 21, 2026. Move to 19.5.1, 19.4.3, or 19.3.6 where those apply. Other lines move to 19.2.9 or 19.1.9. Remaining lines move to 19.0.10 or 18.11.13.
Joaxcar reported the flaw through HackerOne. The CVE record credits that report to GitLab.
What the timeline means in practice
Critical flaws carry the shortest remediation window in FedRAMP practice. Providers track them in a Plan of Action and Milestones if they slip. A score of 10.0 leaves little room for delay.
The record should show discovery, decision, and closure dates. It should name the affected GitLab version plainly. It should show the fixed version that replaced it.
Auditors read that chain during continuous monitoring reviews. Gaps in dates are hard to explain later. Clean records make the monthly review simple.
Tooling inside the boundary counts
Some teams list only customer facing services as in scope. Build servers and code hosts then drift outside reporting.
If GitLab builds or stores the service code, it matters. Its compromise can change the code customers run. Boundary reviews should name development platforms directly.
Steps to close this flaw
Inventory self managed GitLab systems in your boundary. Check each version against the affected ranges. Apply the fixed release for each line. Verify the result and close the tracking entry.
Sources
- CVE-2026-110264 record, CVE Program. Updated October 22, 2026.
- GitLab patch release for 19.5.1, GitLab. https://docs.gitlab.com/releases/patches/patch-release-gitlab-19-5-1-released/
- Original diagram by PolicyCortex.
More flaw remediation timeline guides live at fedramp.net.