Questions / Answer
NGINX 9.2 Flaws Start a FedRAMP Remediation Clock
Every flaw notice starts a clock. The teams that track the clock pass review. The teams that do not, explain delays.
On October 14, 2026, F5 published out-of-band security notification K000163408. It fixes three NGINX memory flaws. F5 scores each flaw 9.2 under Common Vulnerability Scoring System (CVSS) version 4.0. NGINX itself rates them medium. Log both scores with the notice date. The clock starts there, not at your next scan.
The three flaws
Common Vulnerabilities and Exposures (CVE) is the public record system. All three flaws are unauthenticated and network reachable. None needs user interaction. All three carry high attack complexity.
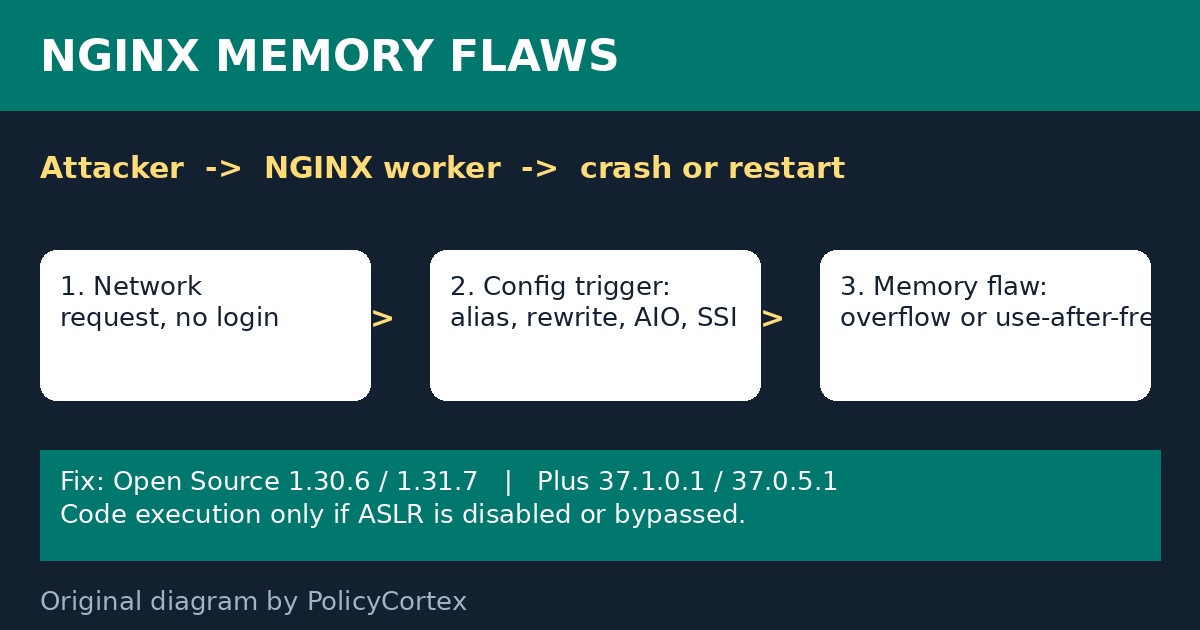
- CVE-2026-15176: heap buffer overflow in the core HTTP module, triggered by alias and rewrite directives using $request_filename.
- CVE-2026-97205: use-after-free flaw, needing asynchronous file input/output (AIO) with Server Side Includes (SSI) virtual includes.
- CVE-2026-93479: heap buffer overflow from premature regex map capture references and certain non-cacheable variable expressions.
The main impact is a worker process crash or restart. Code execution needs Address Space Layout Randomization (ASLR) disabled or bypassed. Note that limit in the ticket. It shapes risk, not the deadline.
Fixed builds are NGINX Open Source 1.30.6 and 1.31.7, and NGINX Plus 37.1.0.1 and 37.0.5.1.
How to run the clock
Open one ticket per flaw, or one ticket listing all three. Record the notice date, October 14, 2026. List each affected server and its version. Add the config trigger check per server. Record the upgrade date per server. Close the ticket only with the dated re-scan result.
No confirmed exploitation was reported through October 20, 2026. The Cybersecurity and Infrastructure Security Agency (CISA) Known Exploited Vulnerabilities (KEV) catalog does not list them. An open ticket with no owner is still a finding at review time. Assign it now.
Sources
- F5 security notification K000163408, NGINX Open Source and NGINX Plus vulnerabilities, October 14, 2026.
- CVE-2026-15176 record, CVE Program.
- CVE-2026-97205 record, CVE Program.
- CVE-2026-93479 record, CVE Program.
- Original diagram by PolicyCortex.
Next step
Want remediation clocks tracked without chasing spreadsheets? See how PolicyCortex collects it from live systems.