Questions / Answer
Patch the Identity Broker First: Okta Access Gateway 2026.10.2
Some systems deserve the front of the patch queue. The identity broker is one of them.
On October 22, 2026, Okta Trust published two security advisories for Okta Access Gateway (OAG). OAG is an appliance that puts Okta sign on in front of company apps. Its Admin Console manages that setup.
The two flaws
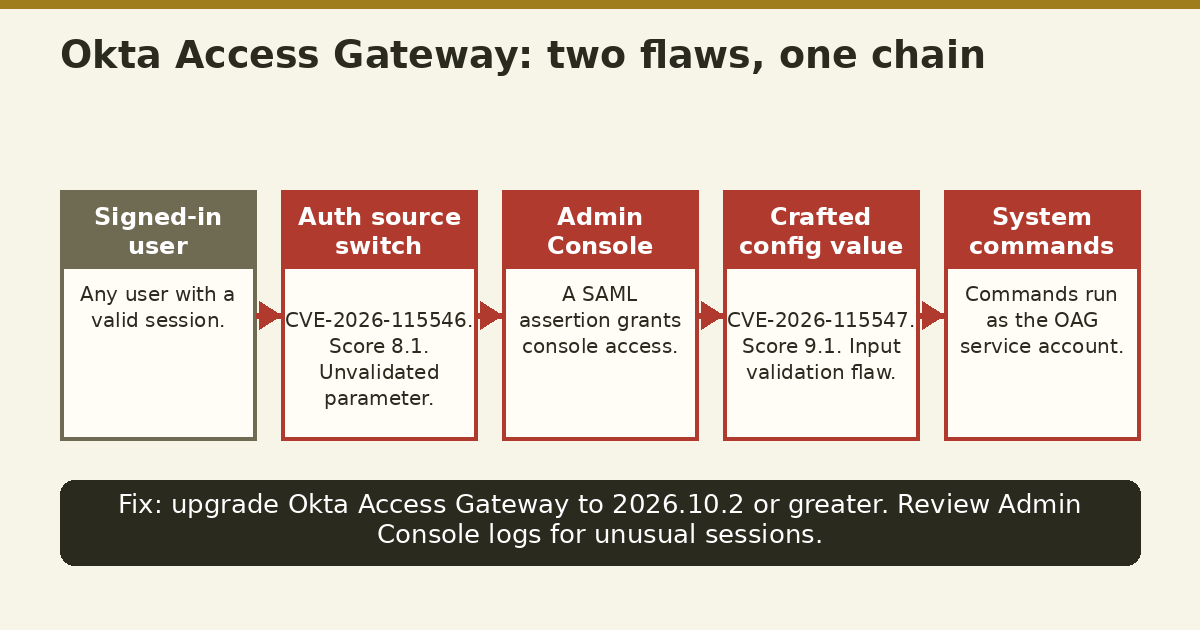
The first record is CVE-2026-115547. Common Vulnerabilities and Exposures (CVE) is the public record system. It is an input validation failure in the Admin Console. An authenticated administrator can use crafted configuration values to run system commands as the OAG service account. The score is CVSS 3.1 9.1, critical.
The second record is CVE-2026-115546. A signed-in user can change the auth source parameter at sign on. The gateway then issues a SAML assertion for the Admin Console. Security Assertion Markup Language (SAML) is the login token standard. The score is CVSS 3.1 8.1, high.
The chain is the point. The 8.1 flaw hands over the console. The 9.1 flaw turns that access into command execution. Both are fixed in OAG 2026.10.2.
Why the broker goes first
FedRAMP flaw remediation runs on risk order. A critical flaw in the system that brokers every login outranks a critical flaw in one app. Compromise the broker and every downstream app inherits the risk.
Your monthly conmon package should show this pair near the top. Continuous monitoring (conmon) is the monthly evidence cycle. The package should show the appliance in the scan inventory, the upgrade ticket, and the Admin Console log review.
Neither CVE is in the CISA KEV catalog as of October 23, 2026. No exploitation has been reported. Patch in this window and the entry closes quietly.
If either flaw is still open at month end, it belongs on the Plan of Action and Milestones (POA&M). A POA&M tracks known flaws and their fixes. Identity flaws should carry the shortest milestone dates on that list.
PolicyCortex does not patch Okta appliances. Your team applies vendor fixes. PolicyCortex helps organize the evidence that follows.
What to do this week
Upgrade OAG to 2026.10.2 or greater. Review Admin Console logs back to October 1.
Sources
- Okta Trust security advisory, Command Execution via Admin Console Input in Okta Access Gateway, October 22, 2026.
- Okta Trust security advisory, Authentication Source Verification Issue in Okta Access Gateway, October 22, 2026.
- CVE-2026-115547 record, CVE Program.
- CVE-2026-115546 record, CVE Program.
- Original diagram by PolicyCortex.
Next step
Want conmon evidence assembled from live systems each month? See how PolicyCortex collects it automatically.