Questions / Answer
Pillow 13.0.0: Remediation Clocks Start With a Version List
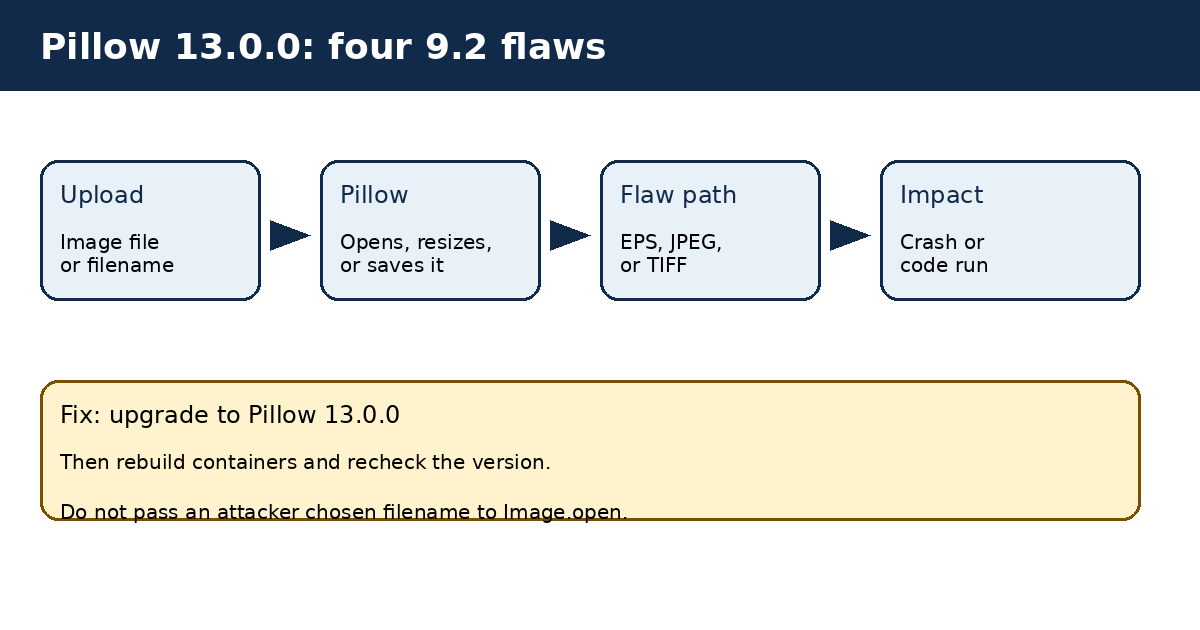
Federal Risk and Authorization Management Program (FedRAMP) work runs on continuous monitoring. A new critical flaw starts a clock. The clock is only useful if you know where the flaw lives.
Pillow is a Python imaging library. It opens, converts, resizes, and saves images. Pillow 13.0.0 arrived October 16, 2026. It fixes four flaws scored 9.2.
The four flaws
Common Vulnerabilities and Exposures (CVE) is the public record system. The Common Vulnerability Scoring System (CVSS) rates severity from 0 to 10.
- CVE-2026-112900: EPS filename injection into Ghostscript.
- CVE-2026-112398: FlashPix JPEG heap overflow on a normal open.
- CVE-2026-112403: Lossless JPEG heap overflow on draft or thumbnail.
- CVE-2026-112393: TIFF save heap overflow to memory.
Each flaw is a scanning finding until it is fixed. A scanner that misses bundled Pillow copies misses the finding. Check containers, wheels, and vendored code.
What continuous monitoring needs
Open a remediation item per affected service. Record the Pillow version found. Record the date the item opened. Record the upgrade date to Pillow 13.0.0. Test first, because version 13.0.0 drops Python 3.10.
Rebuild container images that carry Pillow. Recheck the version after deploy. Close the item only with the recheck result attached. An item closed on a ticket alone will not survive review.
If a service cannot upgrade at once, record the interim control. Removing Ghostscript from an upload host counts. Renaming uploads to a safe name counts. Set a date to revisit the item. A dated interim control beats an open item with no owner.
No wild exploitation is reported in the advisories checked. None of the four IDs is in the CISA Known Exploited Vulnerabilities catalog as checked October 25, 2026. Use the quiet window to patch.
Sources
- Pillow 13.0.0 release notes, October 16, 2026.
- CVE-2026-112900 record, CVE Program.
- CVE-2026-112398 record, CVE Program.
- CVE-2026-112403 record, CVE Program.
- CVE-2026-112393 record, CVE Program.
- Original diagram by PolicyCortex.
Next step
Want remediation evidence linked to each control? See how PolicyCortex collects it from live systems.