Questions / Answer
Plex2Shell and the FedRAMP Remediation Clock
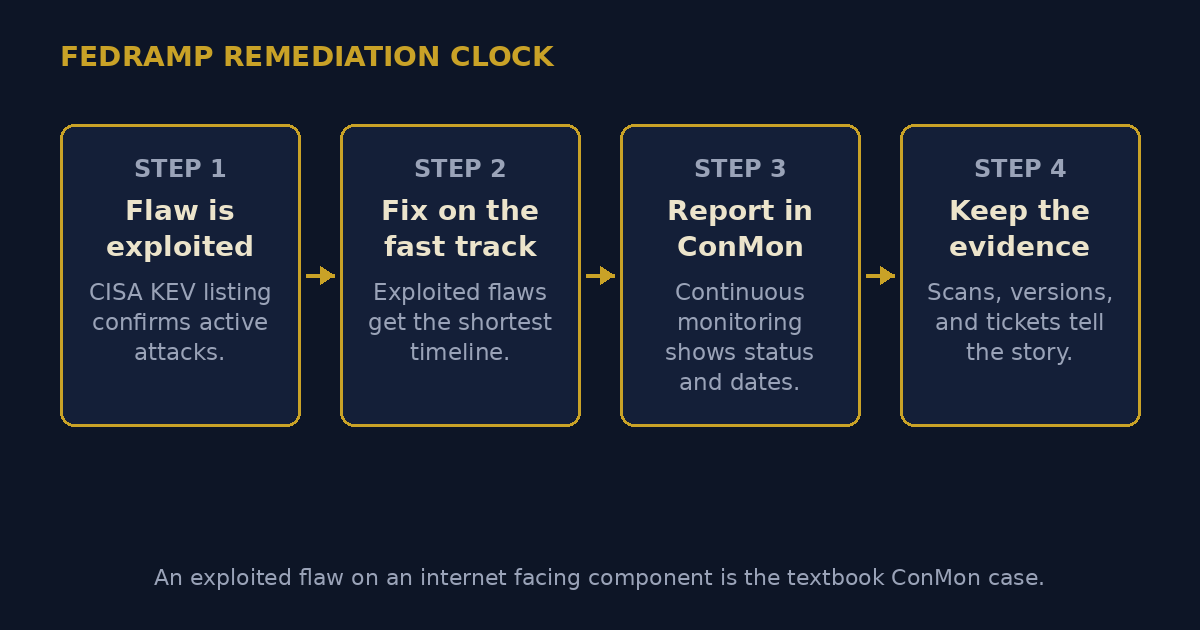
FedRAMP continuous monitoring runs on deadlines. Plex2Shell shows how fast those deadlines arrive in real life.
On October 20, 2026, CISA added four Plex Media Server flaws to its Known Exploited Vulnerabilities catalog. The flaws are CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656. (CISA alert) CISA told federal agencies to patch or mitigate by October 23.
That is three days from confirmed exploitation to the federal deadline.
What continuous monitoring asks for
FedRAMP is the Federal Risk and Authorization Management Program. Continuous monitoring, called ConMon, is the monthly proof that an authorized service stays secure.
ConMon requires cloud service providers to remediate vulnerabilities on set timelines. High risk flaws get the shortest window. An exploited flaw on an internet facing component is the highest priority case.
Plex is not a FedRAMP authorized service. The lesson still applies. Every authorization boundary has internet facing components. When CISA confirms exploitation, the timeline starts.
Why exploited beats scored
ConMon plans often rank work by severity scores. Plex2Shell breaks that habit. Each flaw alone scores medium or high. The chained result is remote code execution with no login.
An exploited medium beats an unexploited high. The catalog is the signal. When a flaw enters it, move it to the front of the line whatever its score.
What the monthly deliverable should show
The ConMon package shows the flaw, the affected asset, the remediation action, and the date. For a KEV listing, also show the exposure check. Name which assets faced the internet, and whether compromise was possible.
Plex's own guidance says older internet facing servers should be treated as possibly compromised. A ConMon record that shows the patch but skips the compromise check is half done.
What to do this week
Check your authorization boundary for Plex Media Server or similar internet facing media services. Confirm builds against 1.43.3.10861.
Record the check with dates. Even a clean result belongs in the package.
Sources
- CISA Adds Six Known Exploited Vulnerabilities to Catalog, CISA, October 20, 2026. https://www.cisa.gov/news-events/alerts/2026/10/20/cisa-adds-six-known-exploited-vulnerabilities-catalog
- CVE-2026-96656 record, CVE Program. https://www.cve.org/CVERecord?id=CVE-2026-96656
- FedRAMP Continuous Monitoring guidance, FedRAMP. https://www.fedramp.gov/continuous-monitoring/
- Original diagram by PolicyCortex.
Next step
Want continuous monitoring evidence collected from your live cloud configuration? See how PolicyCortex does it on Azure.