Questions / Answer
KEV Timelines Bind FedRAMP Providers Too
Federal Risk and Authorization Management Program (FedRAMP) runs on deadlines. A Known Exploited Vulnerabilities (KEV) listing sets a hard one.
The Cybersecurity and Infrastructure Security Agency (CISA) listed two flaws together. The listing date was October 13, 2026. The federal due date was October 16, 2026.
The two listings
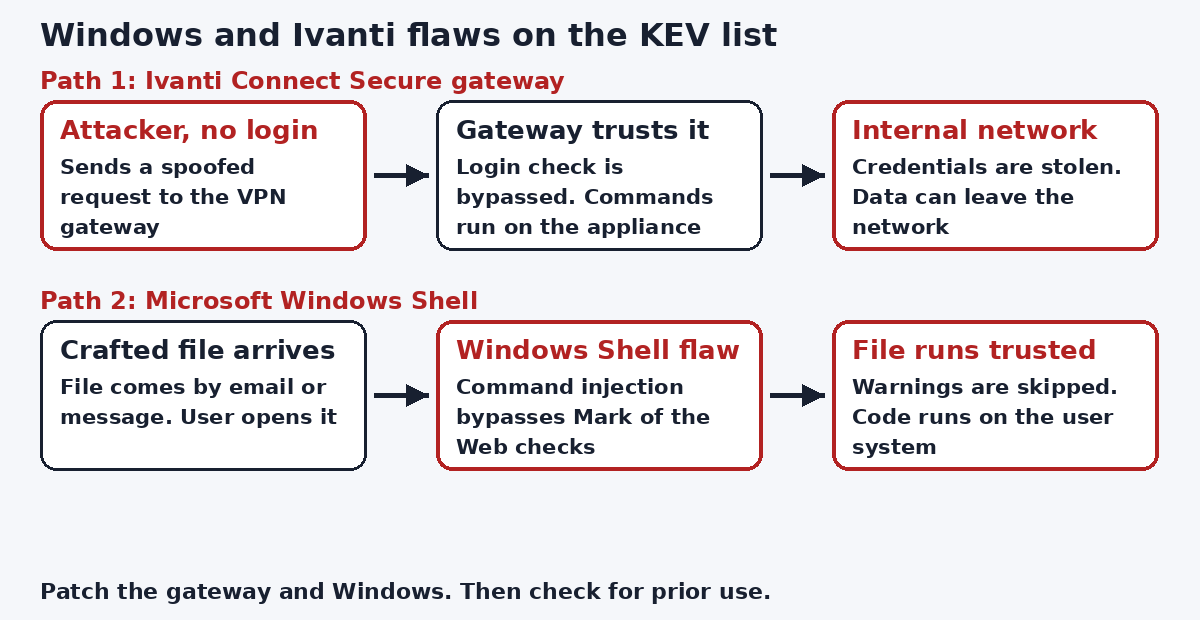
The Windows record is CVE-2026-96951. Common Vulnerabilities and Exposures (CVE) is the record system. It is a Windows Shell command injection flaw.
The Ivanti record is CVE-2026-104935. It is a login bypass in Ivanti Connect Secure. A remote attacker can run commands without login.
Connect Secure is a Virtual Private Network (VPN) gateway. Many providers place such gateways at their boundary. That placement raises the remediation stakes here.
Where the timeline duty comes from
Binding Operational Directive (BOD) 22-01 created the KEV duty. It told federal agencies to fix listed flaws by set dates. Current KEV entries cite BOD 26-04 instead.
The National Vulnerability Database entry shows that action. It tells agencies to follow vendor instructions. It also tells them to complete forensics triage.
FedRAMP providers follow agency remediation expectations too. Their authorization depends on timely flaw correction. A missed KEV date becomes a plan item. It can also become an authorization risk.
Why three days matters
Three days leaves no room for monthly cycles. Providers need an asset list that is already current. They need owners named before the listing lands.
For the Ivanti flaw, patching is not enough alone. CISA warns the vendor checker may miss exploitation. Attacker commands can execute in memory only.
Providers should pair the patch with a hunt. Network and memory forensics are CISA guidance here. The hunt result belongs in the remediation record.
PolicyCortex does not patch Windows or Ivanti products. Vendors ship those fixes. PolicyCortex helps teams collect remediation evidence.
Note on PolicyCortex status: PolicyCortex is not FedRAMP authorized. This article explains duties for FedRAMP providers generally.
What to do this week
Match every boundary gateway against affected builds. Match every Windows asset against the October update. Record the fix date and the hunt result.
Sources
- CVE-2026-96951 record, CVE Program. Updated October 21, 2026.
- CVE-2026-104935 record, CVE Program. Updated October 13, 2026.
- CVE-2026-104935 detail, National Vulnerability Database. KEV due date October 16, 2026.
- CISA Urges Patching Newly Exploited Vulnerability in Ivanti Connect Secure, CISA, October 13, 2026. https://www.cisa.gov/news-events/alerts/2026/10/13/cisa-urges-patching-newly-exploited-vulnerability-ivanti-connect-secure
- Original diagram by PolicyCortex.
Next step
Want KEV remediation dates tracked against live assets? See how PolicyCortex collects that evidence on a schedule.